A reinstall gives your machine a fresh operating system. On a bare-metal server you choose the image, the disk partitioning, and which SSH keys and post-install scripts go on, then the installer runs for up to fifteen minutes. On a cloud instance it's called a rebuild, and the disk is recreated from a template in a few minutes.
Every disk is erased. There is no undo and no automatic snapshot. Back up what you need before you start. On a cloud instance you can take a snapshot or backup ahead of the rebuild. On a bare-metal server, copy the data off yourself.
Settle three things first:
- How will you log in afterwards? If you supply SSH keys, root on the new system accepts those keys and nothing else. If you don't, we generate a root password, show it to you once on the page and hold on to it for 48 hours.
- The hostname. Use a fully-qualified name (
web1.example.com, notweb1). It becomes both the machine's name and its reverse DNS, which is why a bare label won't do. - Apps staged from the App Library get installed as part of this reinstall or rebuild, and the page lists which ones. Don't want them? Cancel them on the Apps tab before you begin.
Method 1: In the portal
Bare-metal servers
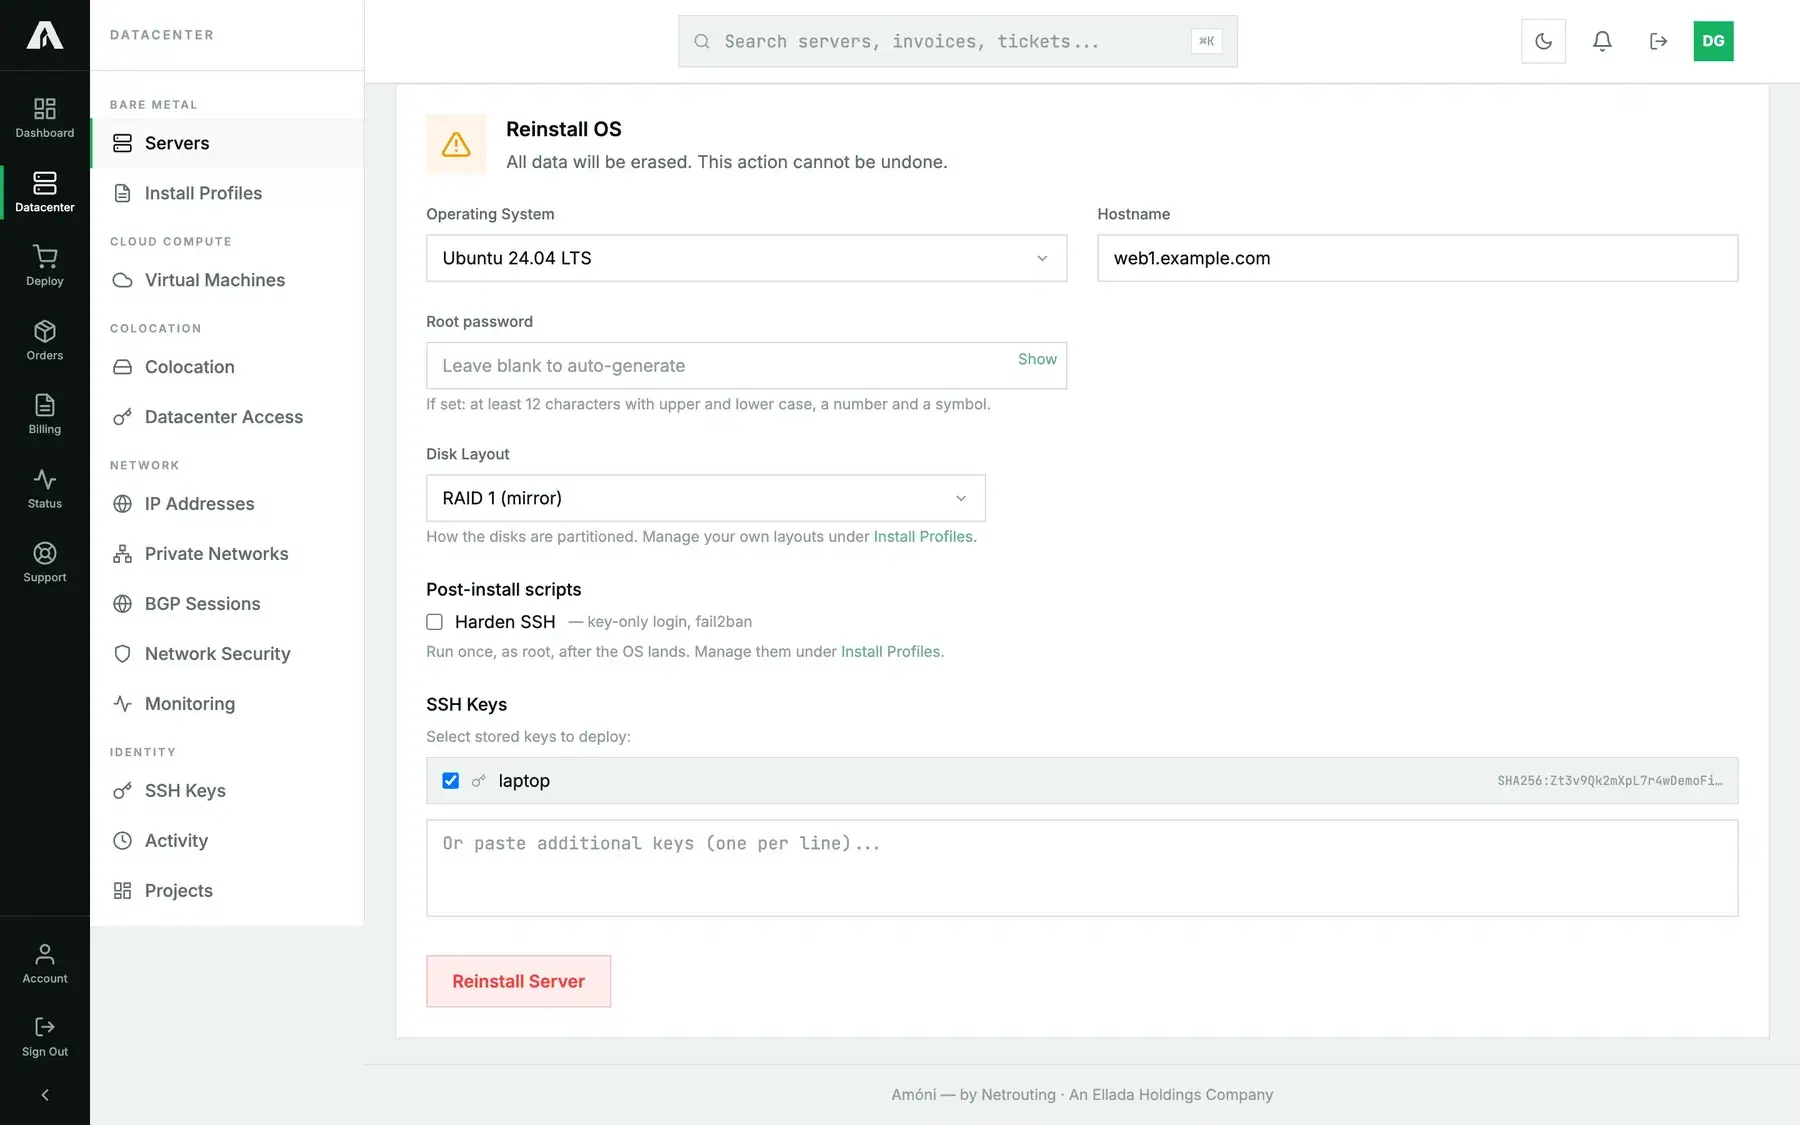
- Log in at amoni.app, open Servers, click the server, and go to the Reinstall tab.
- Under Operating System, choose the image. The list only holds what this machine can install, and Windows images show up where there's a license for them.
- Hostname starts out as the current name. You can change it, provided it stays fully qualified.
- Leave Root password empty and one is generated for you. Your own needs at least 12 characters, with upper and lower case, a number and a symbol. The form tells you what's still missing as you type.
- Under Disk Layout, Default partitioning keeps the image's own scheme. Standard layouts are the RAID and single-disk schemes the platform provides, and Your layouts are whatever you built yourself under Install Profiles.
- Tick any Post-install scripts that should run once, as root, after the OS is in place. You can pick up to five, and you manage them under Install Profiles.
- Tick stored keys under SSH Keys, or paste extra public keys, one per line. The form flags a malformed key while you're still typing.
- Click Reinstall Server. The installer starts right away.
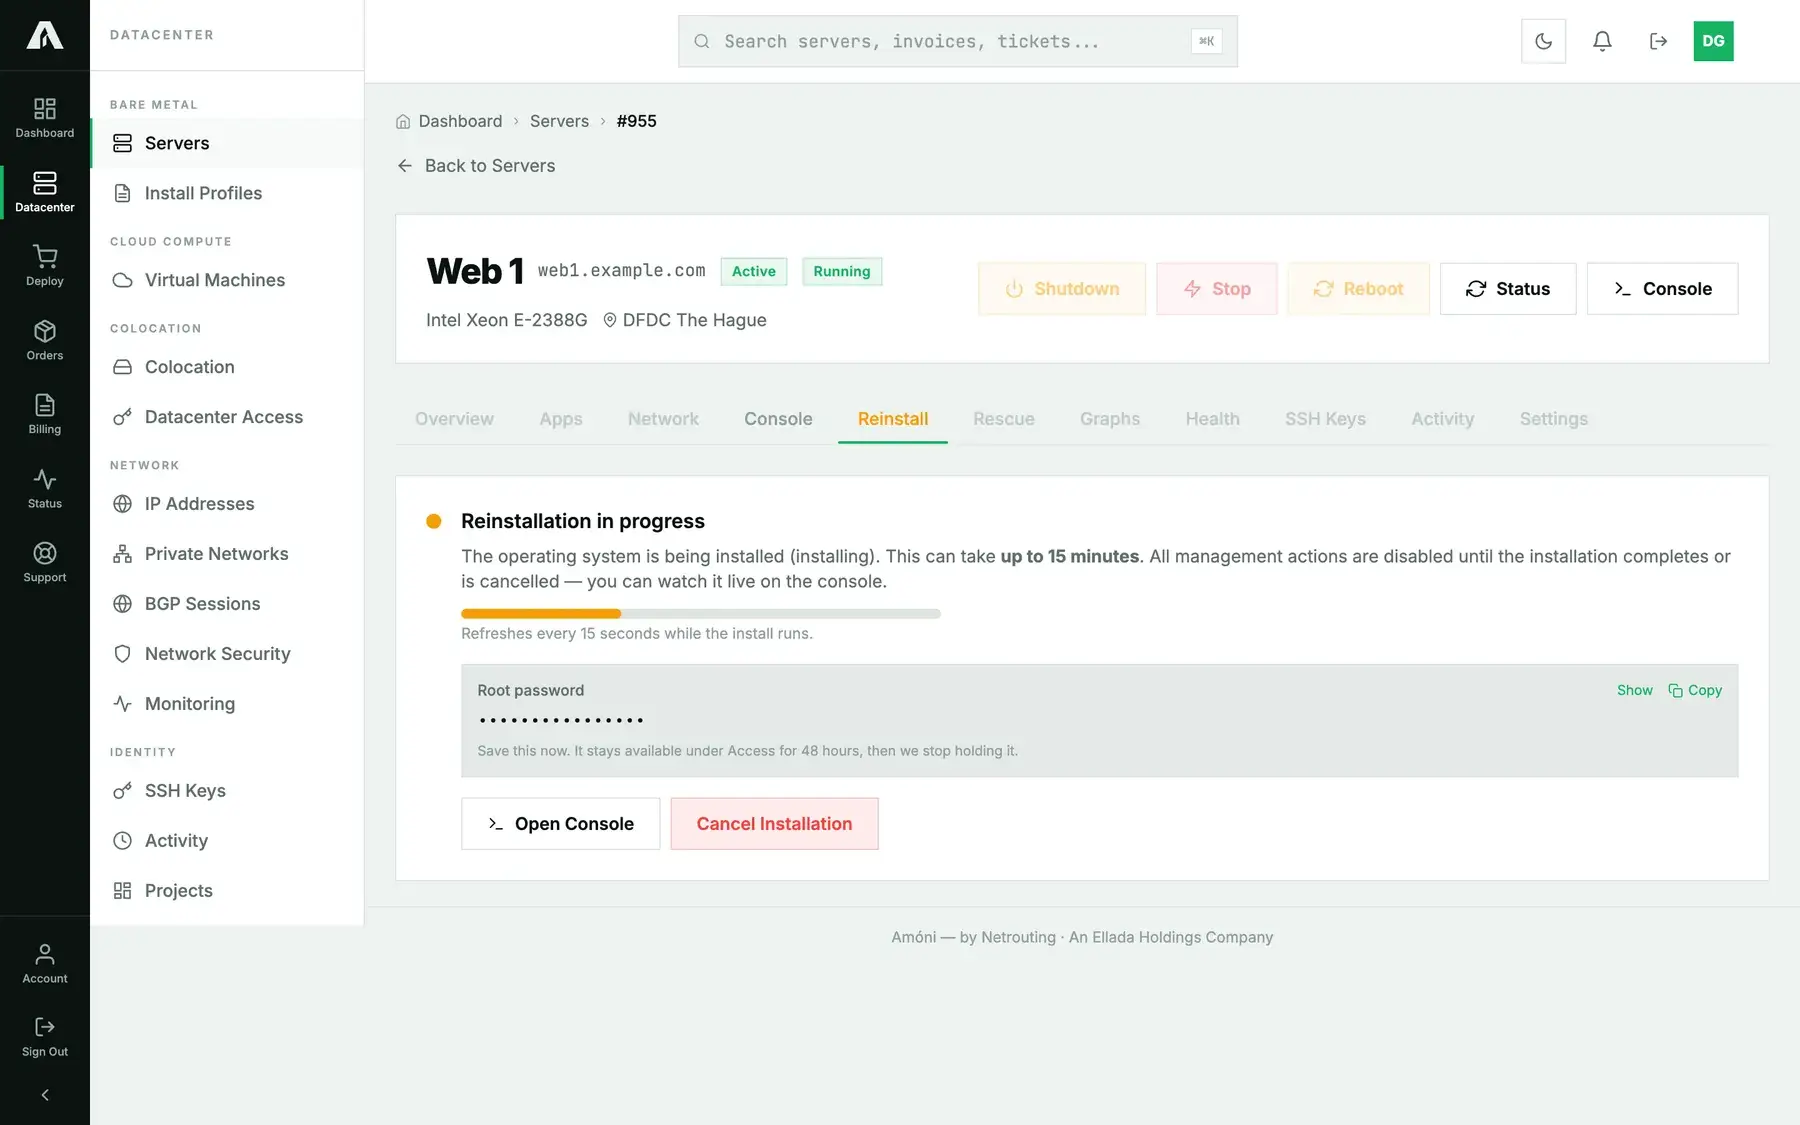
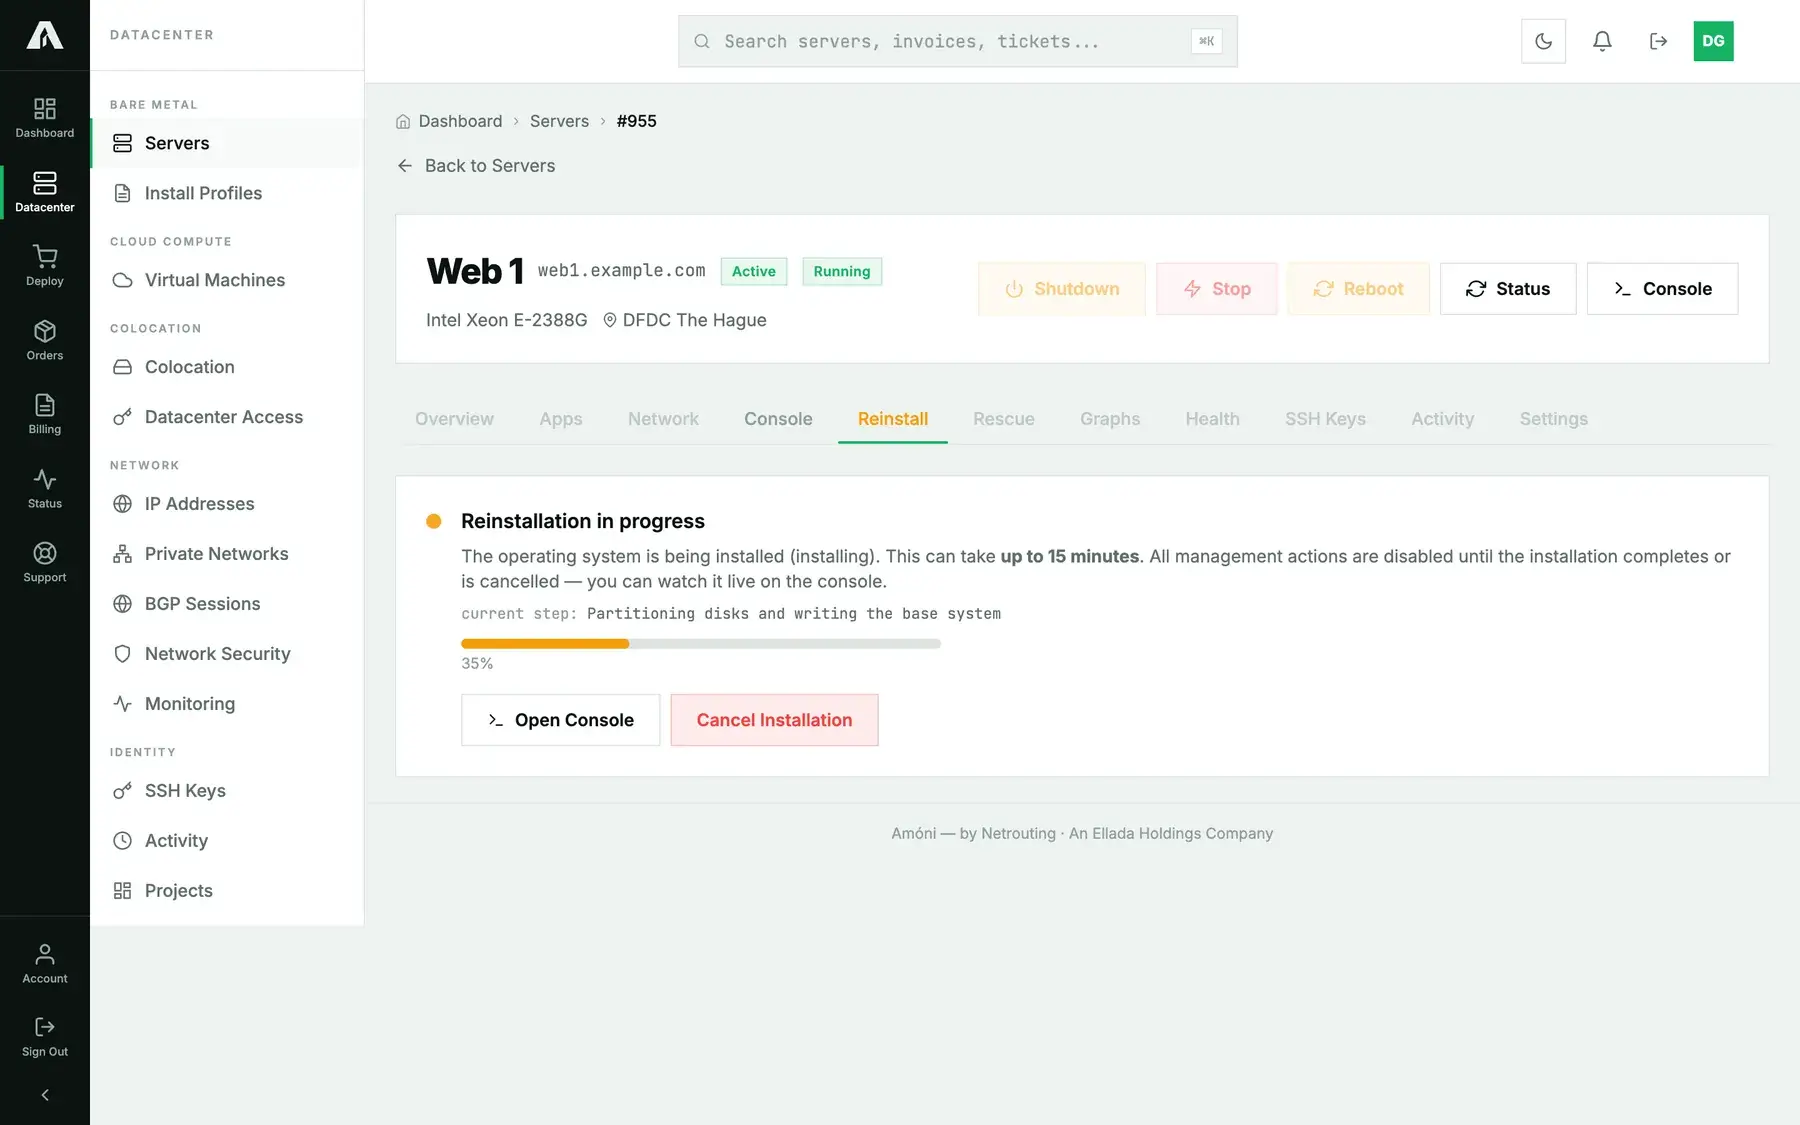
The page changes to Reinstallation in progress and refreshes every fifteen seconds until the installer says it's done. A generated root password appears in this card. Click Show or Copy and save it now. Every other management action is locked while the install runs, but Open Console lets you watch it, and Cancel Installation stops it provided nothing has hit the disk yet.
Once it's done, the other tabs come back and the Overview lists the new OS. Access on the Overview tab keeps the generated root password for 48 hours. Change it as soon as you're logged in, and after that we don't keep a copy.
Cloud instances
- Open Virtual Machines, click the instance and go to the Rebuild tab.
- Click Rebuild VM to open the dialog.
- Choose an operating system template.
- Tick stored SSH keys or paste in public keys. With no key, you get into the new system with a root password you fetch after the rebuild.
- Click Rebuild. The red line in the dialog is the only warning left.
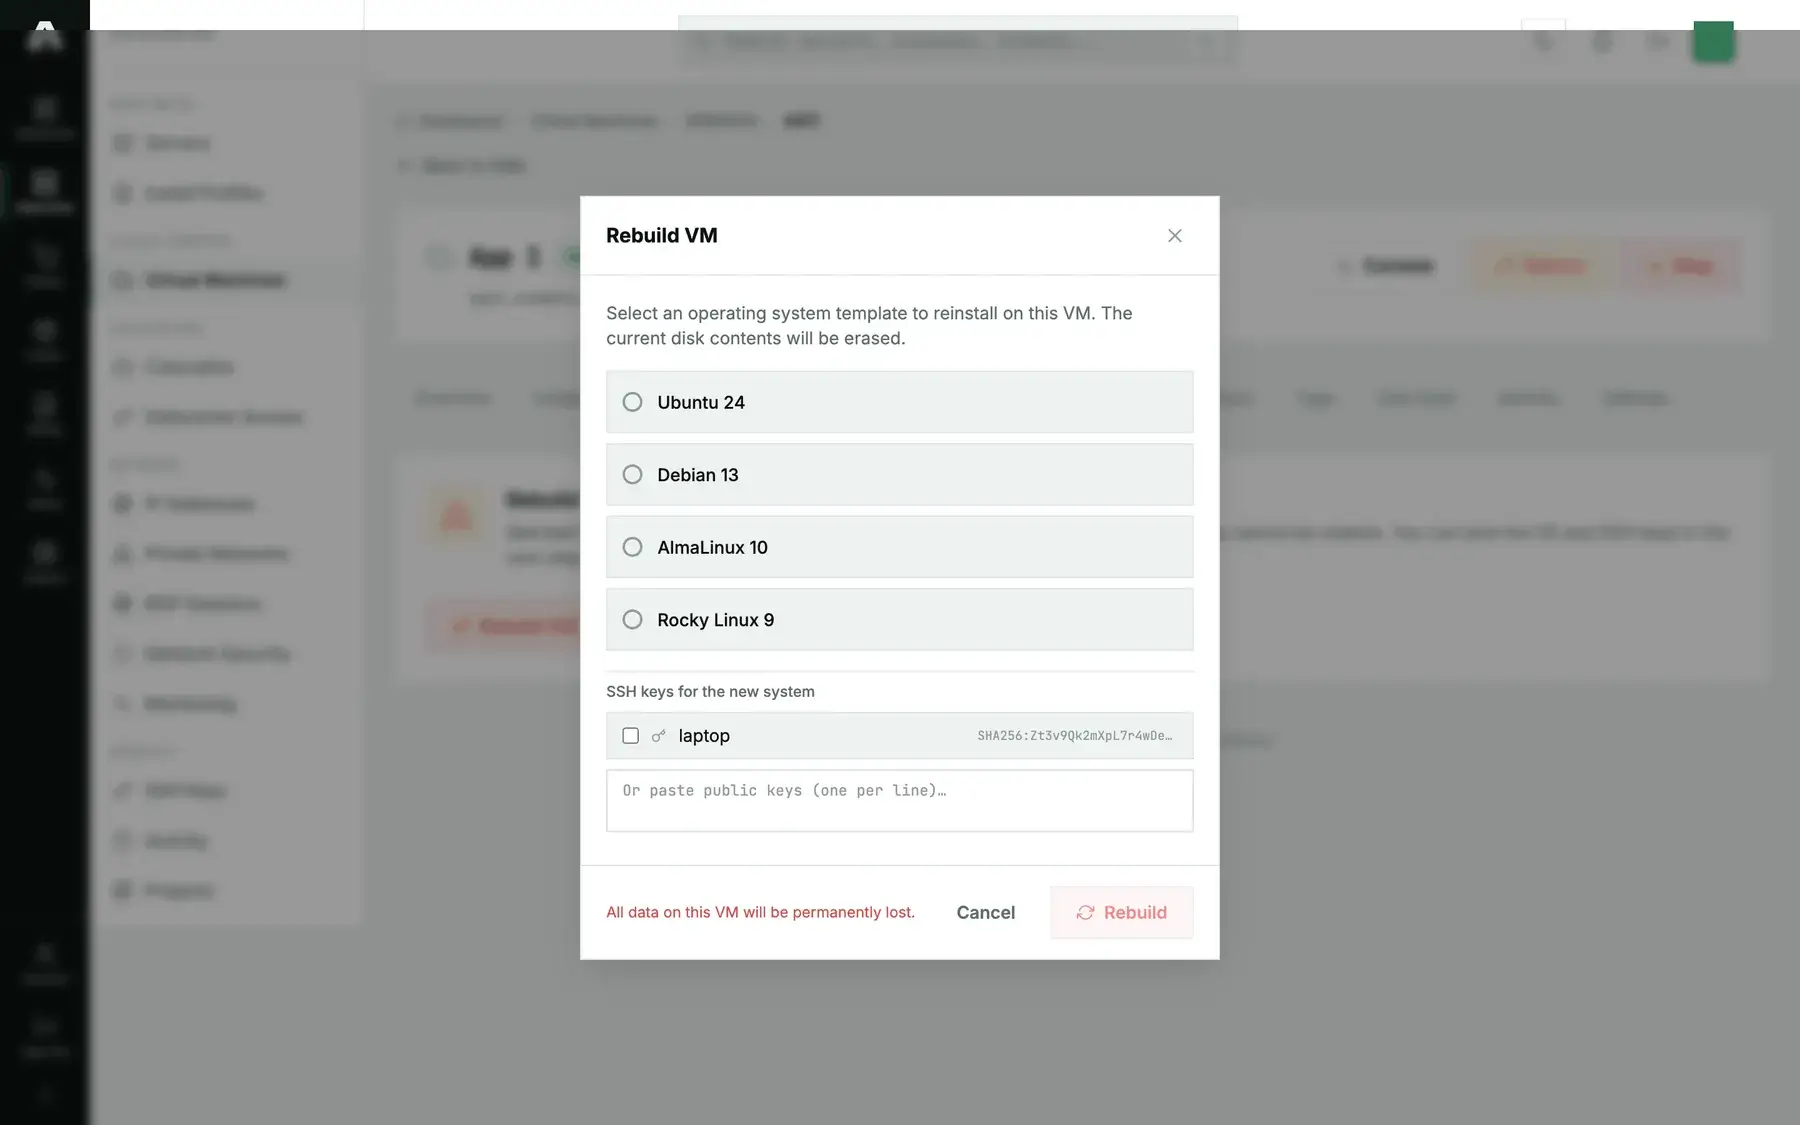
The page reports VM rebuild initiated and follows the operation until it either succeeds or fails. Power actions stay locked until then. The new system boots on its own. No key? Use reset password under Access to get a root password.
Method 2: With the API
Your API key needs the Servers scope (servers.write) or the VMs scope (vms.write). Reference: api.amoni.app/v1/docs.
Bare metal
1. See what the server can install. A single call returns the profiles, our standard disk layouts, your own layouts and your scripts:
curl -s https://api.amoni.app/v1/servers/955/profiles \
  -H "Authorization: Bearer nr_live_..."
{
"success": true,
"data": {
"profiles": [ { "id": 11, "name": "Ubuntu 24.04 LTS", "os_slug": "ubuntu2404" }, { "id": 12, "name": "Debian 13", "os_slug": "debian13" } ],
"standard_layouts": [ { "id": 1, "name": "RAID 1 (mirror)" }, { "id": 2, "name": "RAID 0 (stripe)" } ],
"disk_layouts": [ { "id": 301, "name": "LVM, separate /var", "scope": "client" } ],
"scripts": [ { "id": 501, "name": "Harden SSH", "scope": "client" } ],
"utility": [ { "id": 90, "name": "Rescue system (Linux)" } ]
}
}2. Start the reinstall. profile_id is the one required field. Send tos_disklayout_id for a standard layout or disk_layout_id for one of yours, but not both. Stored keys go in ssh_key_ids (take the ids from /v1/ssh-keys), and pasted keys go in sshkeys.
curl -s -X POST https://api.amoni.app/v1/servers/955/reinstall \
  -H "Authorization: Bearer nr_live_..." \
  -H "Content-Type: application/json" \
  -d '{
    "profile_id": 11,
    "hostname": "web1.example.com",
    "tos_disklayout_id": 1,
    "ssh_key_ids": [42],
    "script_ids": [501]
  }'
{
"success": true,
"data": {
"message": "Reinstall started. This can take several minutes.",
"notice": null,
"applied": {
"os": "Ubuntu 24.04 LTS",
"disk_layout": "RAID 1 (mirror)",
"hostname": "web1.example.com",
"root_password_set": true,
"root_password_generated": false,
"ssh_keys": [ { "name": "laptop", "fingerprint": "SHA256:..." } ],
"pasted_key_count": 0
}
}
}Don't assume, read applied: it's the record of what really went onto the machine. If something got dropped (keys the installer refused, say), notice explains it in one sentence. When you sent no password and no keys, root_password_generated is true and applied.root_password carries the generated password once.
3. Wait for it. The call comes back the moment the installer accepts the job, long before the install is done. Poll the installation status until complete is true:
until curl -s https://api.amoni.app/v1/servers/955/provision-status \
        -H "Authorization: Bearer nr_live_..." | jq -e '.data.complete == true' >/dev/null; do
  sleep 30
done
echo "installed"
During the install the payload includes status, step and, if the installer reports one, percentage. To abort before anything touches the disks: POST /v1/servers/955/reinstall/cancel.
4. Fetch the generated password, if any. We hold it for 48 hours and then throw it away. Because of what this endpoint returns, it needs servers.write.
curl -s https://api.amoni.app/v1/servers/955/root-password \
  -H "Authorization: Bearer nr_live_..."
A 404 with code: root_password_unavailable means it has expired or was never generated. After you've saved it somewhere, you can drop our copy early with DELETE on the same path.
Cloud instances
1. List templates:
curl -s https://api.amoni.app/v1/vms/990204/411/templates \
  -H "Authorization: Bearer nr_live_..."
{ "success": true, "data": [ { "vmid": 9001, "name": "ubuntu-24.04" }, { "vmid": 9002, "name": "debian-13" } ] }2. Rebuild. This call is asynchronous. It answers 202 with an operation:
curl -s -X POST https://api.amoni.app/v1/vms/990204/411/rebuild \
  -H "Authorization: Bearer nr_live_..." \
  -H "Content-Type: application/json" \
  -d '{"template_vmid": 9001, "ssh_key_ids": [42]}'
{
"success": true,
"data": {
"message": "Rebuild started. This wipes the current system and takes several minutes.",
"operation": { "id": 7731, "status": "pending" }
}
}3. Poll the operation until status is succeeded or failed:
curl -s https://api.amoni.app/v1/operations/7731 -H "Authorization: Bearer nr_live_..."{ "success": true, "data": { "id": 7731, "type": "vm.rebuild", "status": "running", "resource_type": "vm", "resource_id": 411,
"message": null, "result": null, "started_at": "2026-09-15 11:26:10", "finished_at": null, "created_at": "2026-09-15 11:26:02" } }GET /v1/operations returns the account's recent operations in the same shape, newest first. Power actions and reverse DNS changes show up there as well.
4. Password. Sent no keys? Then a root password was generated. Use GET /v1/vms/990204/411/root-password after the operation succeeds. The 48-hour rule from bare metal applies here too.
What the API will tell you
| Status | Meaning |
|---|---|
| 200 / 202 | Accepted. Bare metal replies 200 with applied, cloud replies 202 with an operation. |
| 401 / 403 | The key is bad, or it lacks servers.write / vms.write. |
| 403 | This server is managed infrastructure, so reinstall is turned off for it. Contact support. |
| 404 | Your account has no such server, VM or operation. Body: {"success": false, "error": "Not found"}. |
| 409 | The layout or script you picked exists but can't be used yet (it has no partitioning content, or hasn't synced). The error text says which one. |
| 422 | Validation. Field checks arrive in the framework shape, such as a hostname that isn't fully qualified: {"message": "The hostname must be a fully qualified domain name — \"web1\" has no domain. Try \"web1.example.com\".", "errors": {…}}, or a template_vmid under 100. Rule checks arrive in the envelope: a weak password, an unknown profile, a key that isn't an OpenSSH public key, a layout or script that belongs to someone else, or a server whose state doesn't allow a reinstall. |
| 500 | The installer or hypervisor didn't respond: “Could not read the installation status.” from provision-status, “Templates are unavailable right now. Please retry.” from templates, or the generic “The action could not be completed right now” from reinstall. Try once more, then open a ticket with the time. |
Troubleshooting
- SSH says the host key has changed. That's expected, because a fresh install generates a new host key. Remove the old entry and connect again:
ssh-keygen -R 203.0.113.10 - “Permission denied (publickey)” after reinstalling with keys. This is deliberate. Once you supply keys, root can't log in with a password. Connect with the matching private key (
ssh -i ~/.ssh/id_ed25519 root@203.0.113.10). Wrong key? Reinstall with the right one, or add it through the remote console. - I did not save the generated password. You'll find it under Access on the Overview tab for 48 hours (or at
/root-passwordin the API). Past that, reset it. Cloud instances have reset password under Access. A bare-metal server can be reinstalled, or given a new password from the rescue system. - The hostname was rejected. It has to be fully qualified, with at least one dot, and it may only contain letters, digits and hyphens.
- The page says the install is still in progress long after it should be done. Open the console and look at the screen. That's where you'll spot an installer sitting at a prompt, or a machine that never booted from the network. If it's stuck before anything was written to disk, cancel and start over. If not, open a ticket.
- “This server cannot be reinstalled automatically.” This machine isn't hooked up to the automated installer. Open a ticket and we'll do the reinstall for you.
- My post-install script did not run. If the image you chose doesn't support your script, the reinstall response tells you on the spot (
noticein the API, an amber message in the portal). Check the script's tags under Install Profiles. - Windows: what is the password? It works the same as on Linux. The password is shown once after the reinstall and held for 48 hours. Log in through the remote console or over RDP.
Still stuck?
Open a support ticket from the portal. Select the server in the “related server” field and tell us when you started the reinstall. Your Activity log already holds the attempt and everything it applied.